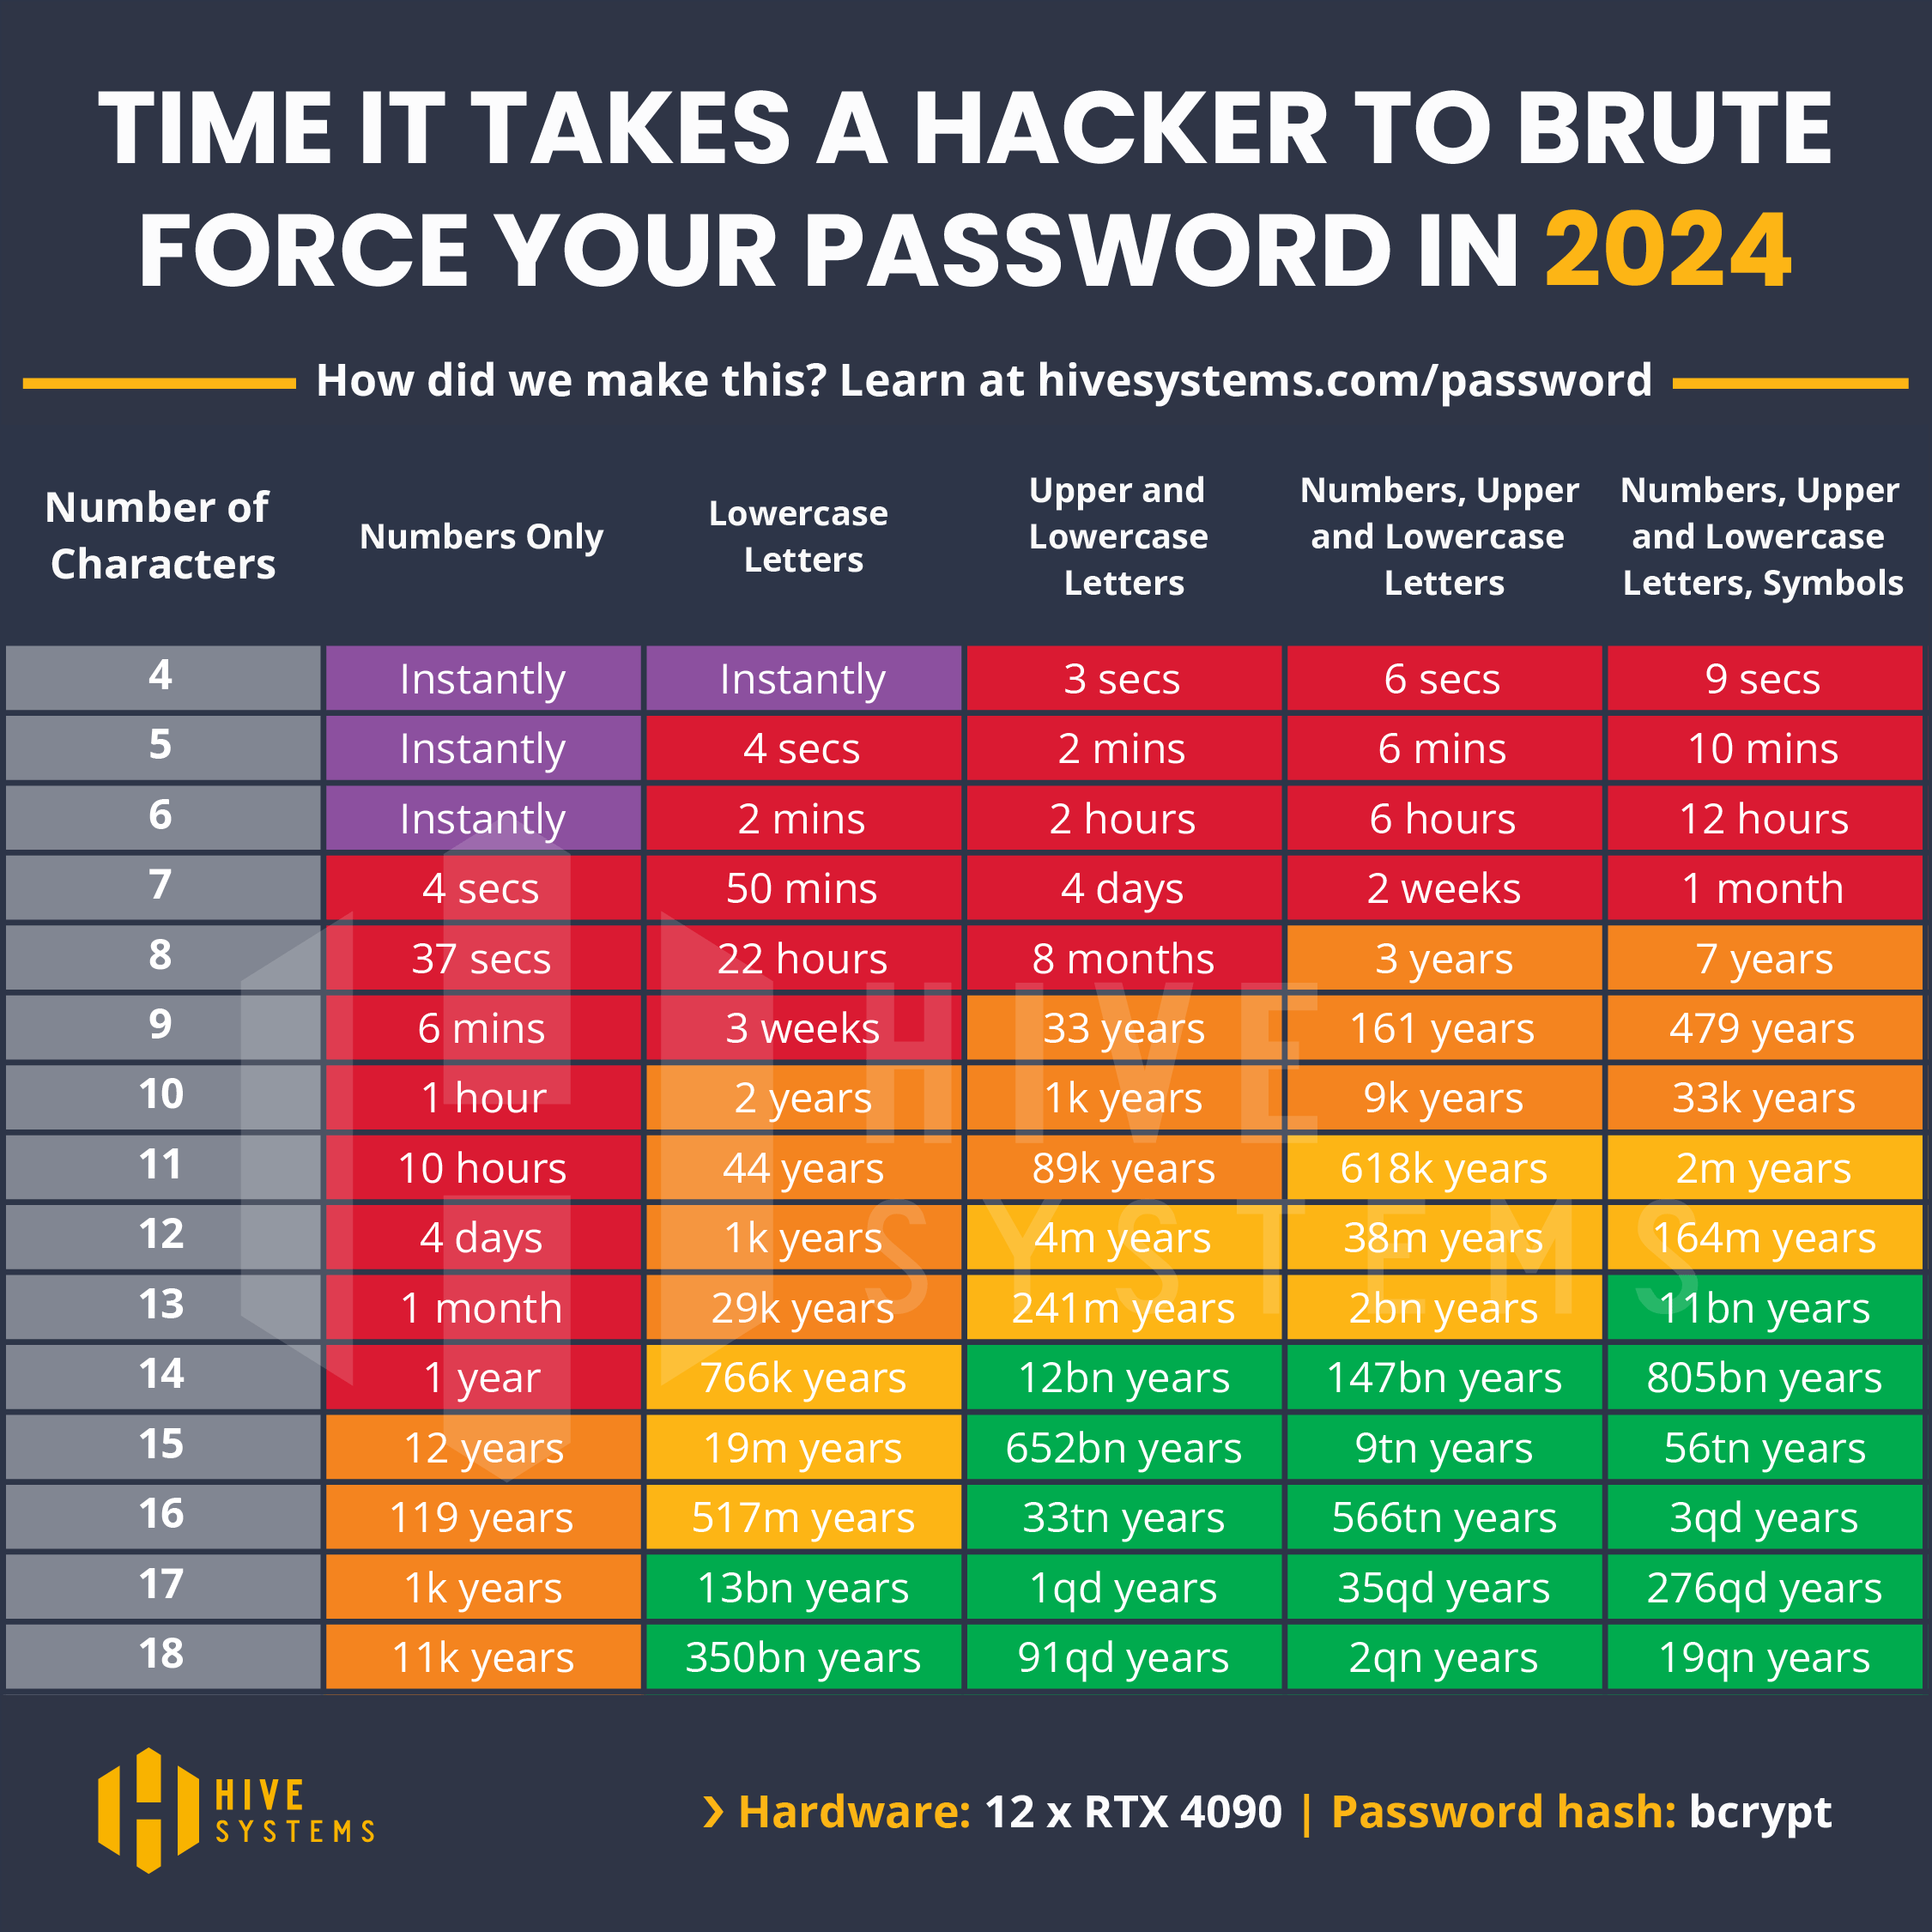
Hi everyone! I’m back again with the 2024 update to our password table!
Computers, and GPUs in particular, are getting faster (looking at you OpenAI), but password hash algorithm options are also getting better (for now…). This table outlines the time it takes a computer to brute force your password, and isn’t indicative of how fast a hacker can break your password – especially if they stole your password via phishing, or you reuse your passwords (shame!). It’s a good visual to show people why better passwords can lead to better cybersecurity – but ultimately it’s just one of many tools we can use to talk about protecting ourselves online!
**Data source:** Data compiled from research using multiple sources about hashing functions, GPU power, and related data. The methodology, assumptions, and more data can be found at [www.hivesystems.com/password](http://www.hivesystems.com/password)
**Tools used:** Illustrator and Excel
gh0stkill3rs on
I guess a lot of people are going to change their passwords
wonderpra on
Wow, yes. Time to change all passwords. Thank you for this.
Glass_Confusion448 on
correct horse battery staple
puntacana24 on
It is amusing to think about a hacker spending 350 billion years trying to crack someone’s password
Rudokhvist on
My passwords are so long they don’t even fit in this table. Of course, only for services that allow it. Recently encountered a site that said „max 12 characters, no special characters, only letters and numbers“. In 2024, for fucks sake!
AnInsultToFire on
In reality, does a brute force attacker start with 4 characters, move up to 5, then 6, then 7?
BiBoFieTo on
If you have 12 RTX 4090s, then wouldn’t you be going after specific high-value targets rather than randos?
lostcauz707 on
When you incorporate 2 factor it’s an insanely long time.
Arowhite on
So you’re telling me that I went too far with my 24-char passwords?
MentalJargon on
Not sure I’m on board with the colouring splits, 1 year as severe as 3 seconds? 2 years equated to 33,000 years?
_Darkrai-_- on
My password is exactly 18 characters with everything so iam sitting in the bottom right corner but also 12 characters are numbers
Good thing about the numbers is there is no reasonable connection its using a word spelt entirely with the letters of chemicals
Shuriin on
Doesn’t this assume the hacker has unlimited login attempts?
dougthebuffalo on
Does „characters“ mean random characters? Is it easier (or harder) to crack a short phrase that meets all other parameters?
Threef on
That’s why you make a 100ms delay on login response, and 1000ms after 5 tries.
It makes even easiest passwords nearly resistant to brute force
AnonUserAccount on
If 9 characters takes 479 years when one of everything is used, then why are some places requiring 15 characters? Those are too hard to remember and writing them down defeats the purpose, so why not just stick to 9?
Phantom15q on
currently watching Mr. Robot so this hits a little harder
SodaWithoutSparkles on
If you are lazy, use just run your old password through base64 as your new password. Good enough for most cases. And you don’t need to remember cryptic passwords too.
You can install dedicated apps to do the conversion and block it from accessing the internet, or just use python/cli to convert it on-the-fly.
PaulAspie on
I had a password that is listed over a billion years in this chart, but it was considered too easy so I had to make one off the bottom of the chart.
philmadburgh on
Does having different types of characters actually help or is it just the option to have non letter characters that makes an impact? Or is the assumption that hackers would try only letters first, numbers and letters second and so on?
Global-Cattle-6285 on
Surely “Password123” takes less than 618k years to break? Do hackers put in popular words into their hacking systems… whatever that might be.
Leave A Reply
Du musst angemeldet sein, um einen Kommentar abzugeben.
21 Kommentare
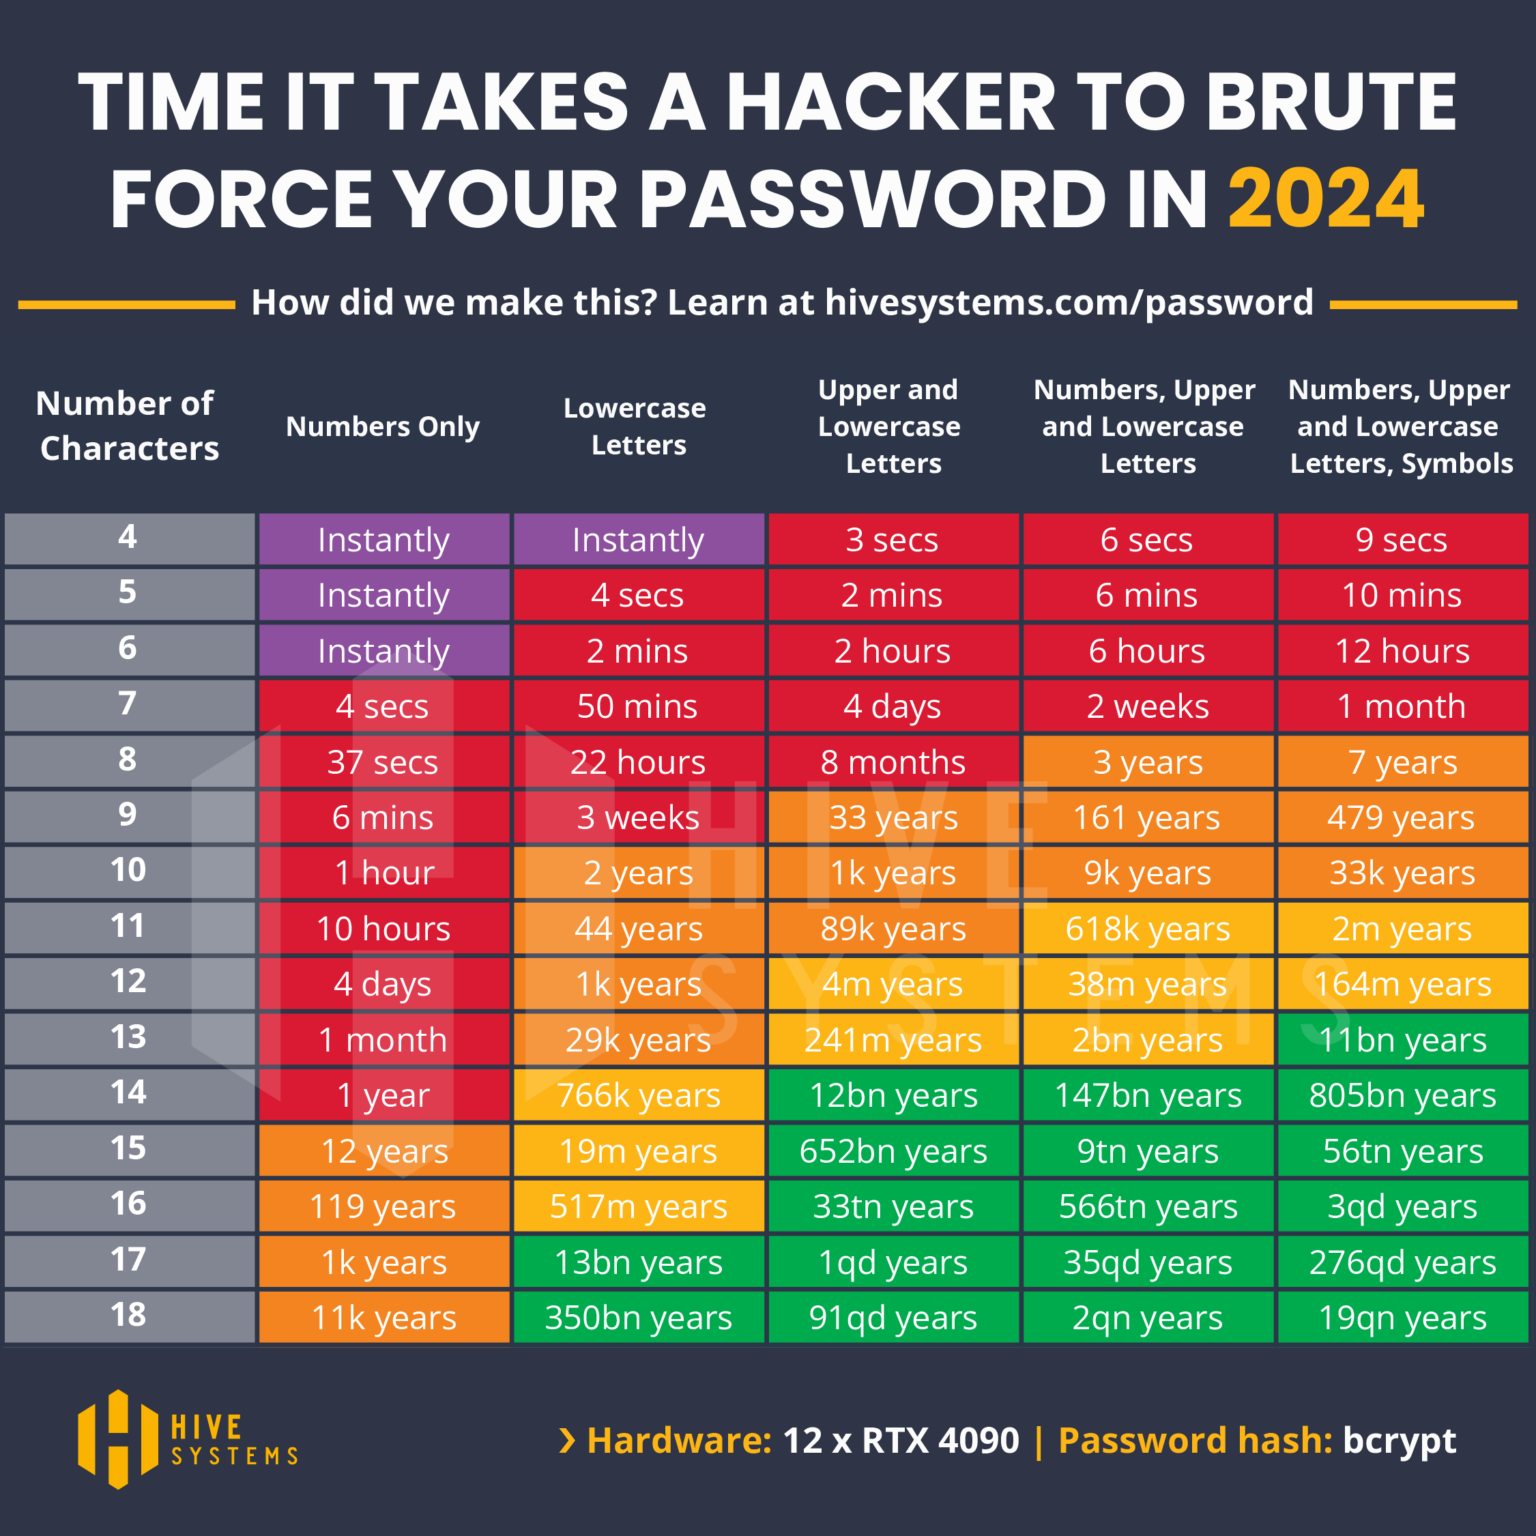
Hi everyone! I’m back again with the 2024 update to our password table!
Computers, and GPUs in particular, are getting faster (looking at you OpenAI), but password hash algorithm options are also getting better (for now…). This table outlines the time it takes a computer to brute force your password, and isn’t indicative of how fast a hacker can break your password – especially if they stole your password via phishing, or you reuse your passwords (shame!). It’s a good visual to show people why better passwords can lead to better cybersecurity – but ultimately it’s just one of many tools we can use to talk about protecting ourselves online!
**Data source:** Data compiled from research using multiple sources about hashing functions, GPU power, and related data. The methodology, assumptions, and more data can be found at [www.hivesystems.com/password](http://www.hivesystems.com/password)
**Tools used:** Illustrator and Excel
I guess a lot of people are going to change their passwords
Wow, yes. Time to change all passwords. Thank you for this.
correct horse battery staple
It is amusing to think about a hacker spending 350 billion years trying to crack someone’s password
My passwords are so long they don’t even fit in this table. Of course, only for services that allow it. Recently encountered a site that said „max 12 characters, no special characters, only letters and numbers“. In 2024, for fucks sake!
In reality, does a brute force attacker start with 4 characters, move up to 5, then 6, then 7?
If you have 12 RTX 4090s, then wouldn’t you be going after specific high-value targets rather than randos?
When you incorporate 2 factor it’s an insanely long time.
So you’re telling me that I went too far with my 24-char passwords?
Not sure I’m on board with the colouring splits, 1 year as severe as 3 seconds? 2 years equated to 33,000 years?
My password is exactly 18 characters with everything so iam sitting in the bottom right corner but also 12 characters are numbers
Good thing about the numbers is there is no reasonable connection its using a word spelt entirely with the letters of chemicals
Doesn’t this assume the hacker has unlimited login attempts?
Does „characters“ mean random characters? Is it easier (or harder) to crack a short phrase that meets all other parameters?
That’s why you make a 100ms delay on login response, and 1000ms after 5 tries.
It makes even easiest passwords nearly resistant to brute force
If 9 characters takes 479 years when one of everything is used, then why are some places requiring 15 characters? Those are too hard to remember and writing them down defeats the purpose, so why not just stick to 9?
currently watching Mr. Robot so this hits a little harder
If you are lazy, use just run your old password through base64 as your new password. Good enough for most cases. And you don’t need to remember cryptic passwords too.
You can install dedicated apps to do the conversion and block it from accessing the internet, or just use python/cli to convert it on-the-fly.
I had a password that is listed over a billion years in this chart, but it was considered too easy so I had to make one off the bottom of the chart.
Does having different types of characters actually help or is it just the option to have non letter characters that makes an impact? Or is the assumption that hackers would try only letters first, numbers and letters second and so on?
Surely “Password123” takes less than 618k years to break? Do hackers put in popular words into their hacking systems… whatever that might be.